

Growing Crisis in Cybersecurity
In January–March 2025, 30,000 information security incidents were recorded in Kazakhstan — 2x more than the same period in 2024.
According to the IBM/Ponemon Institute report, the average total cost of data breaches in 2024 was $4.88 million.
According to Cybersecurity Ventures, global ransomware damage could reach $30 billion by year end.
Cybersecurity in Numbers
In January 2024, 4,200 cyberattacks were recorded in Kazakhstan — twice as many as the previous year (Forbes Kazakhstan).
Kazakhstan ranks 78th out of 175 on the National Cybersecurity Index (ranking.kz).
Over a third (36%) of cybersecurity executives worldwide are not confident in their staff's effectiveness. This highlights the need for continuous training to keep pace with the evolving threat landscape (Kaspersky Lab).
Since January 2023, the GTS team (State Technical Service) has registered approximately 35,000 information security incidents.
In January 2024, 4,200 cyberattacks were recorded in Kazakhstan — twice as many as the previous year (Forbes Kazakhstan).
The Team
The Team
Our company, led by specialists with over 10 years of information security experience, is a resident of the international IT startup technopark «Astana Hub».
We are also an honored participant in the program aimed at developing human capital in IT — «Tech Orda».

 Astana Hub
Our Mission
We believe in the effectiveness of practical training to combat cyber threats.
That's why we created a unique cyber range.
Our team of cybersecurity experts provides high-quality training.
Making the world safer.
What is Interactive Range?
A cybersecurity simulation training platform that offers practical and engaging learning solutions for individuals and organizations looking to develop their cybersecurity skills.
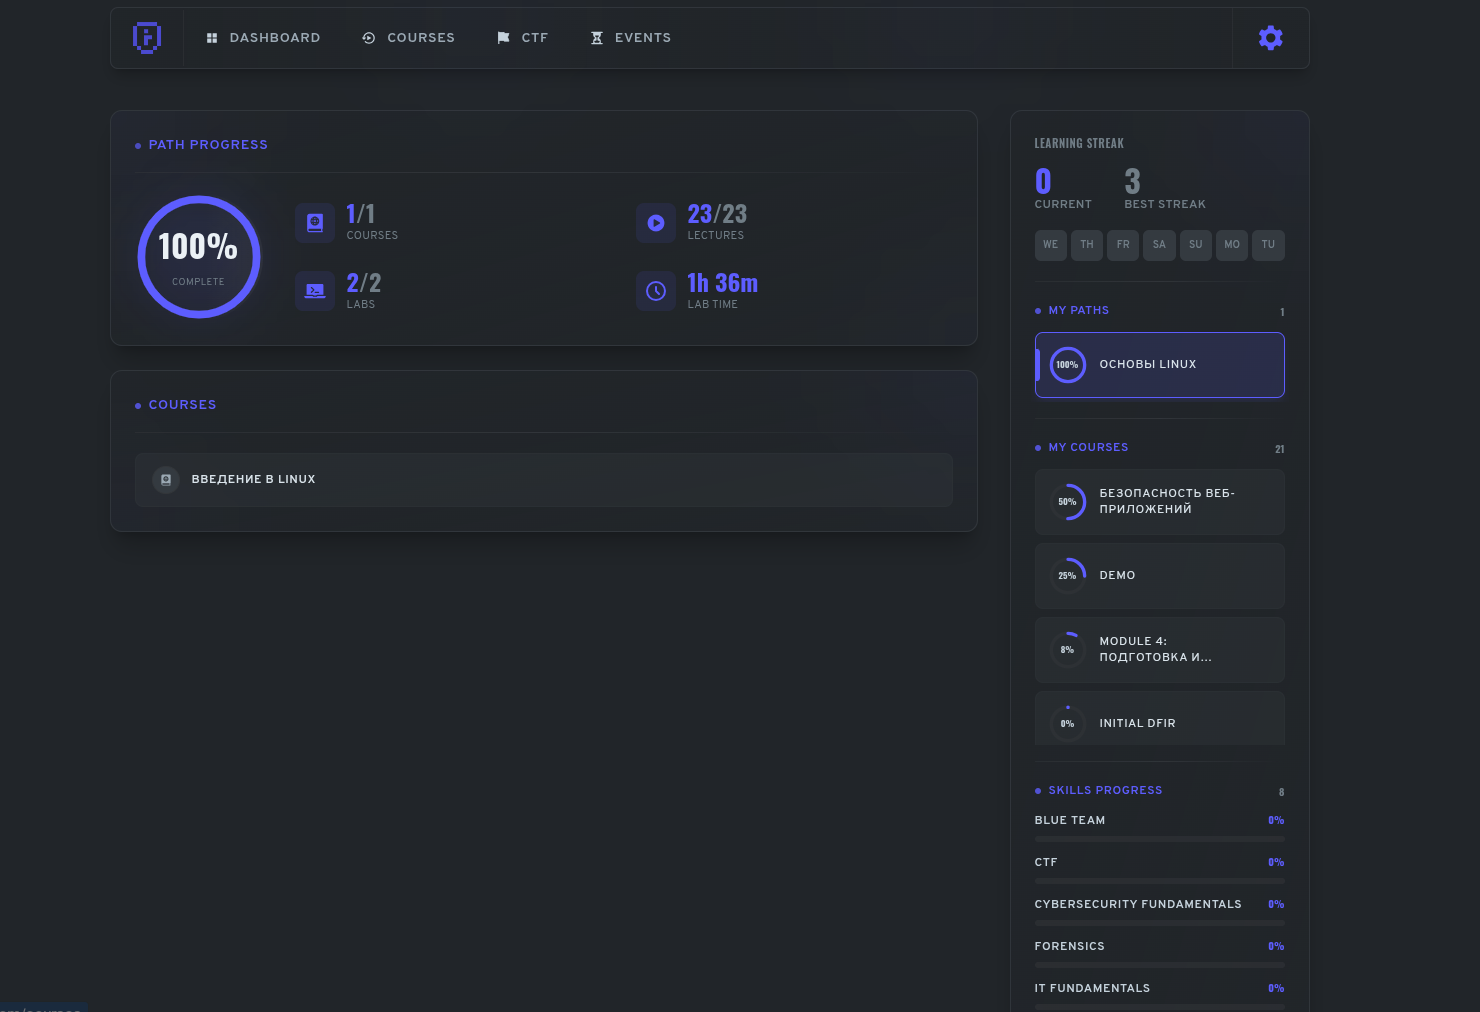
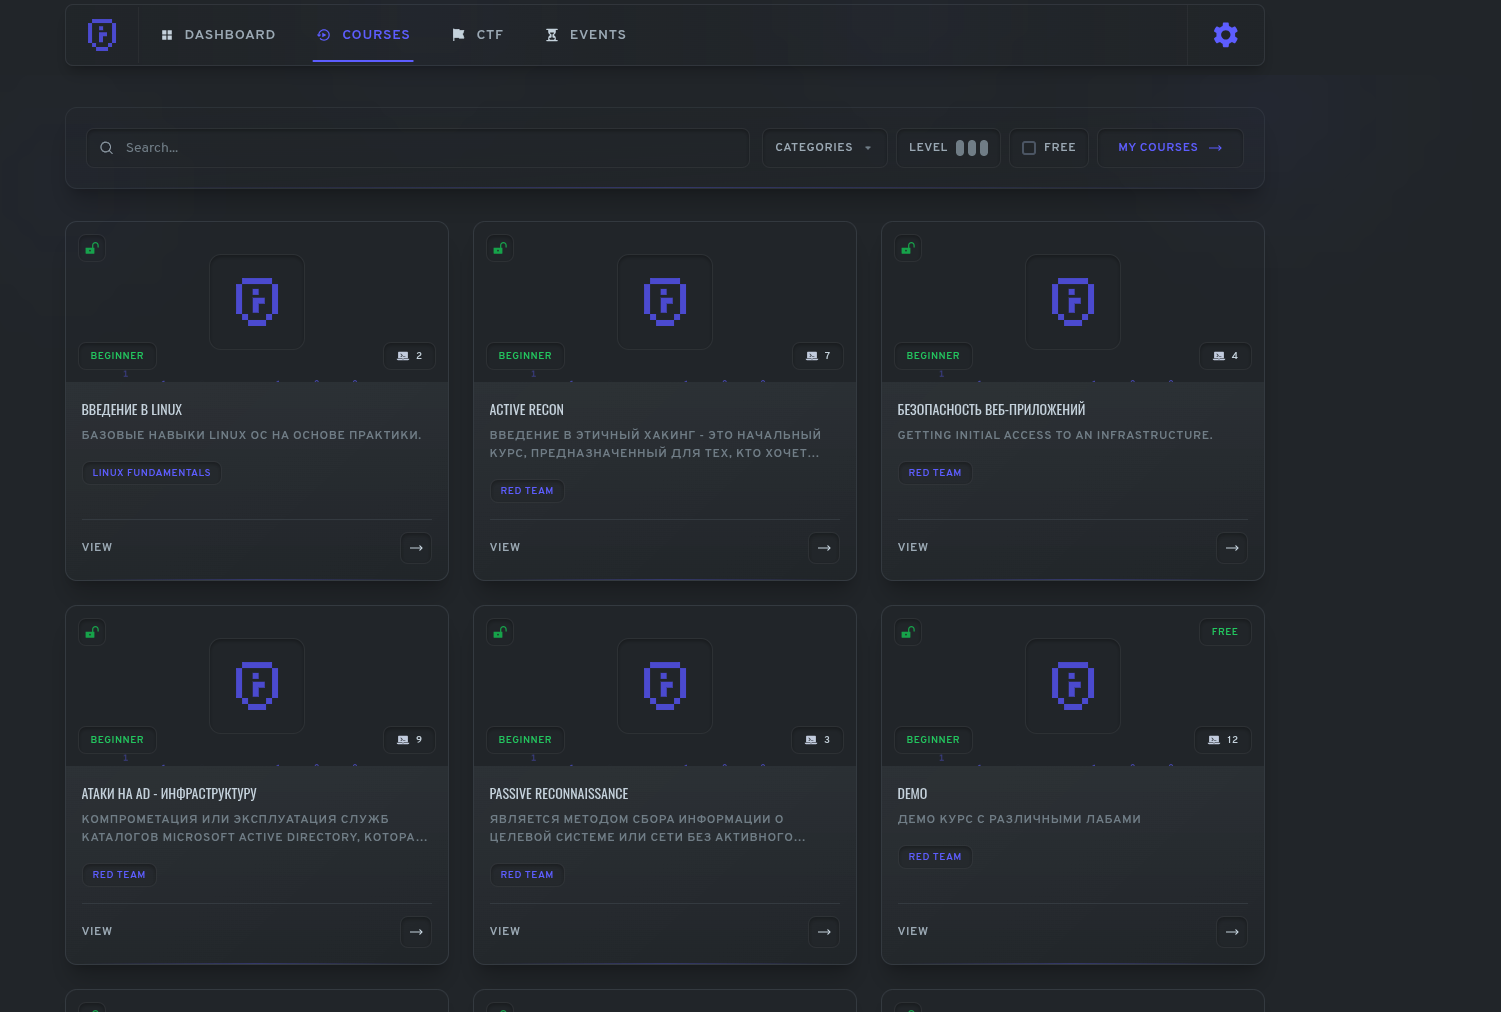
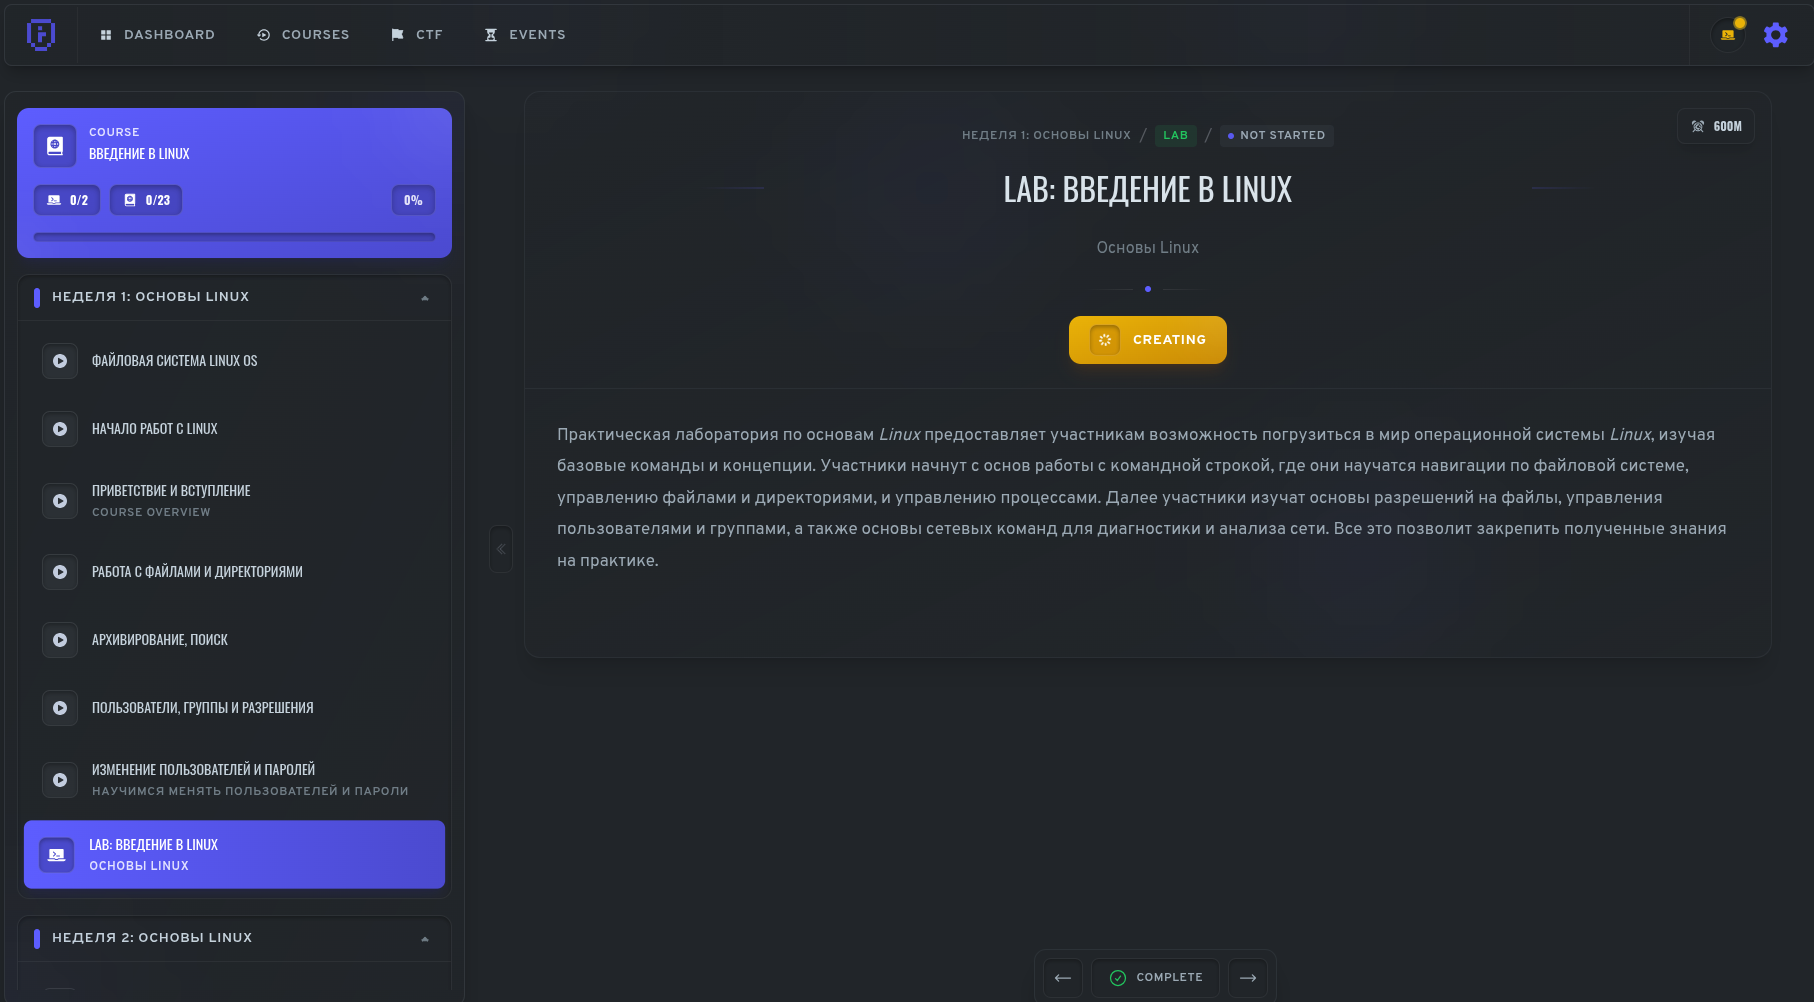
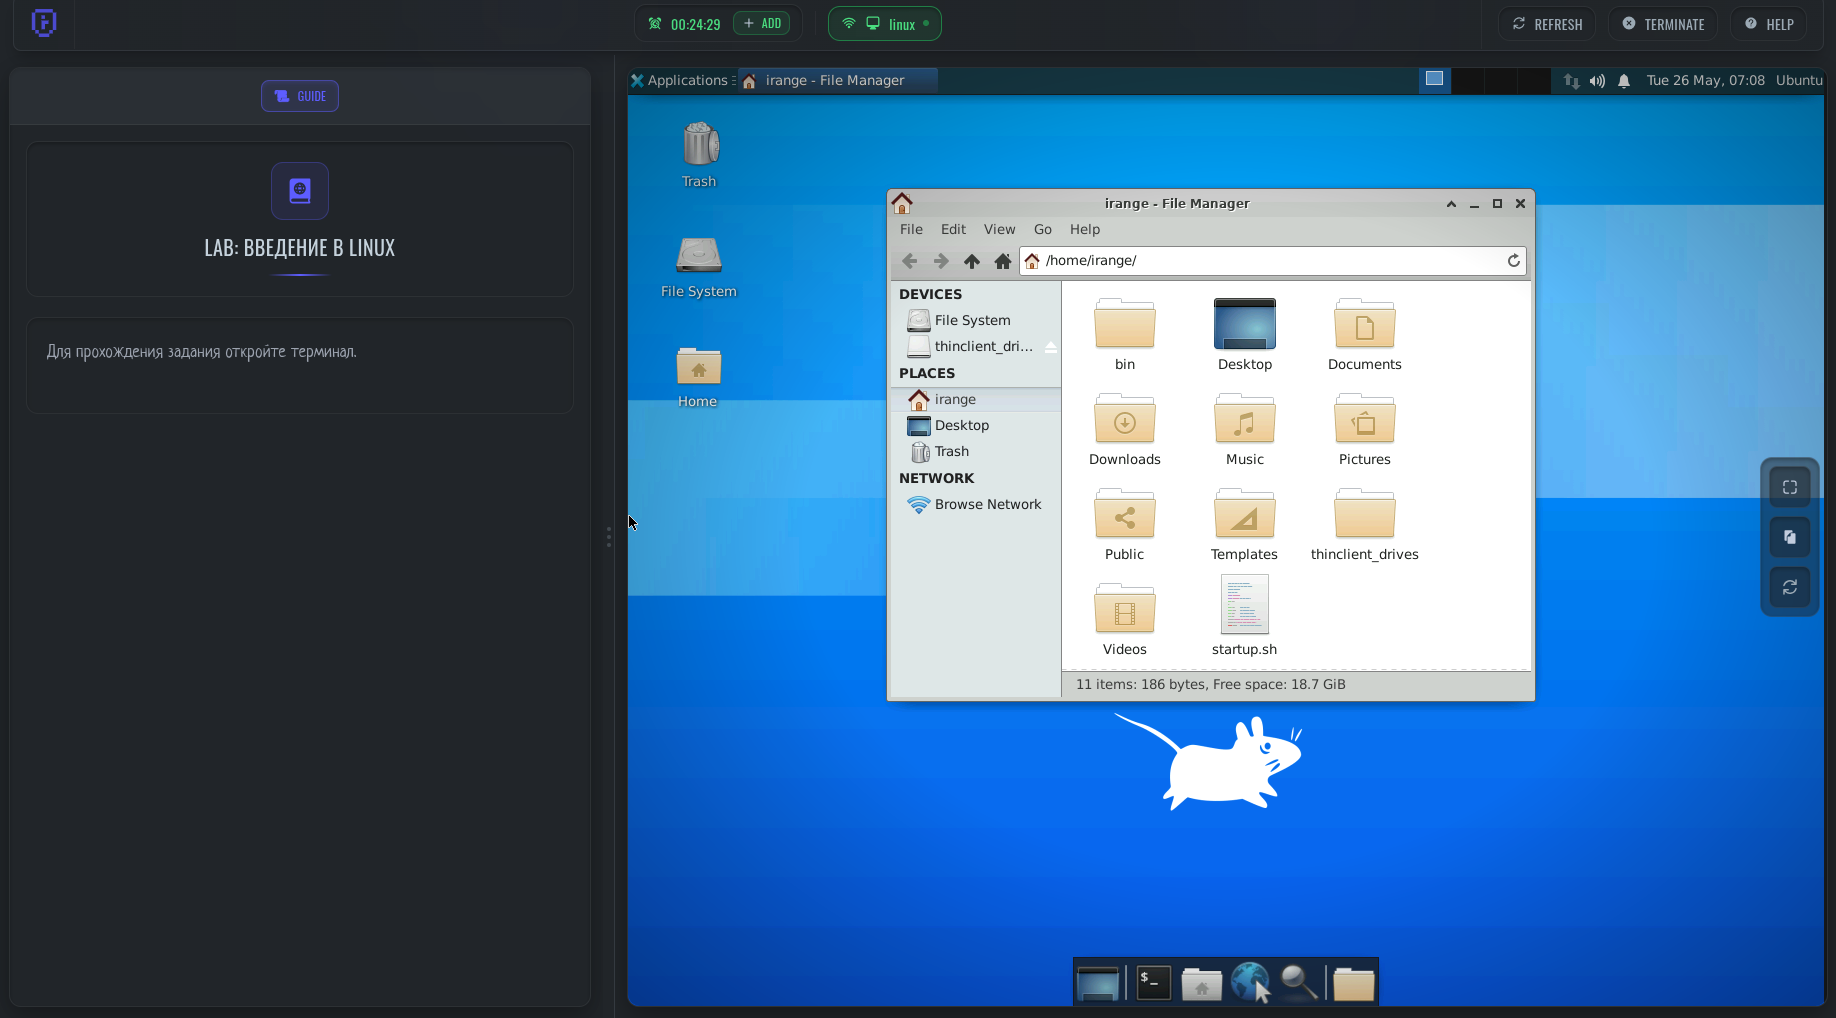
Our platform provides up-to-date content, guided training labs, and analytics and reporting tools that help learners stay ahead and track their progress as they learn.
techordaPage.platform.eventsTitle
techordaPage.platform.eventsText
techordaPage.platform.coursesTitle
techordaPage.platform.coursesText
techordaPage.platform.ctfTitle
techordaPage.platform.ctfText
techordaPage.platform.careerTitle
techordaPage.platform.careerText
techordaPage.platform.scadaTitle
techordaPage.platform.scadaText
techordaPage.platform.cyberagentTitle
techordaPage.platform.cyberagentText
Training Process
Training cybersecurity specialists is analogous to training combat pilots.
To maintain their skills, pilots spend hours training on flight simulators, preparing for any adverse weather conditions or emergencies. The same approach is effective for cybersecurity specialists.
Real security incidents typically start with a software vulnerability that opens an attack vector. Once detected, the attack is analyzed to understand its mechanisms. In response to the incident, the vulnerability is patched to prevent reuse.
This creates three main categories of cybersecurity training.
Attack-oriented training
Defense-oriented training
Analysis-oriented training
Red Team & Blue Team Courses
The «Red Team & Blue Team» course is a comprehensive information security specialist training program combining two tracks: offensive (Red Team) and defensive (Blue Team) cybersecurity.
Red Team
The «Red Team» course builds practical skills in vulnerability discovery and exploitation: network reconnaissance and scanning, MITM attacks, vulnerability assessment and post-exploitation, web application security (OWASP Top 10), Active Directory infrastructure attacks, social engineering, and Bug Bounty fundamentals with real CVE analysis (WebMin, Joomla, Adminer, AppWeb, Jenkins).
Download syllabusBlue Team
The «Blue Team» course develops practical skills in IT infrastructure defense and effective cyber threat countermeasures. Participants study detection and incident response processes using modern tools such as SIEM, IDS/IPS and honeypot, working in a lab environment close to reality. The course examines attack stages through the MITRE ATT&CK lens, including malicious code delivery and execution, as well as prevention methods using YARA and whitelisting policies.
Download syllabusSpecial Conditions: Selection Criteria
To enroll in the course, candidates undergo a preliminary selection process aimed at identifying basic technical knowledge, analytical thinking, and high motivation for development in cybersecurity. Selection is based on candidate resume analysis, considering preparation level, previous experience, participation in specialized projects, competitions, and technical skills. Additionally, results of CTF (Capture The Flag) tasks are evaluated — practical challenges that determine proficiency with information security tools, vulnerability discovery skills, system analysis, and solving non-standard technical problems.
Combat Practice with AI and Anti-AI
Modern APT groups increasingly use generative AI for reconnaissance, phishing, exploit writing, and defense evasion. The program trains specialists to work on both sides of this technology — attacking and defending.
Attacks Using AI
Students will learn in practice how modern adversaries use generative AI to accelerate and amplify their attacks.
Countering AI Threats
In parallel, basic techniques for detecting and defending against attacks using artificial intelligence are practiced.
Platform Advantages
Realistic Environment
Helps specialists better understand real threats and how they might encounter them in real conditions.
Safe Environment
Allows students to learn and experiment without risking damage to real infrastructure.
Ease of Use
We pay special attention to making our platform intuitive for all users — all necessary tools are available by subscription and at hand.
Current Scenarios
Helps specialists prepare for real threats by updating scenarios in line with current trends, improving knowledge applicability.
Scalability
The platform is specifically designed for scalability, enabling large numbers of simultaneous participants.
Cloud Access
Access labs from anywhere in the world via web browser without restrictions.
Unique Platform Features
Wide Selection of Ready-made Scenarios
Our platform offers a huge selection of 75 different scenarios, enabling you to launch a simulation with minimal effort. You can start training in just a few clicks.
Practical Labs for Red & Blue Team at All Levels
The platform offers three courses for each level, from beginner to expert.
24/7 Access
24/7 lab access from anywhere via web browser.
What You Can Become After the Course
Scaling Plans
Creating programs for young specialists
New training directions
Creating a job bank
Building a specialist community
Hosting support events for graduates and students
Daniyar Kasenov — Course Instructor
Daniyar Kasenov
- DEFCON 2016 (Beeline accounts hack)
- DEFCON 2016 Almaty (Buffer Overflow Vulnerability)
- EXPO2017 SOC Expert
- SOCFORUM 2019 (Breaking SOC)
- KAZHACKSTAN 2019 (Threat Hunting in practice)
Certificates
Our instructor holds over 20 international certifications in cybersecurity, networking, and risk management — from Offensive Security and ISC² to Cisco and ISACA.
Start Your Career in Cybersecurity
Combat readiness — 100%. Submit your application to be selected for the TechOrda program.